Pragmatic, sovereign security. Defense by a good offense.
We build defensible security for the new age of AI threats. Practical, EU-sovereign, and shaped by people who attack systems for a living. Less paperwork, more security you can actually stand behind.
Security should be something you operate, not paperwork you file. And the best defense is built by the people who know how to break in.
Four convictions, no compromise.
Sovereignty is a default, not an upgrade
EU-hosted, on our own platform. Your data stays in jurisdiction by architecture, not by promise.
Defense by a good offense
We are offensive specialists first. We find the weaknesses real attackers would, then turn them into controls you run. The best defense is built by people who know how to break in.
Defensible in the AI age
Attackers now move at machine speed and use AI. Defense has to be AI-assisted, continuous and provable. We build security you can demonstrate, not just claim.
Pragmatic over paperwork
Security that lives in spreadsheets protects no one. We make it operational: owned, mapped, evidenced, and actually used.
Why I built Soveryne.
I'm Ilke Tosunoğlu, an ethical hacker and penetration tester based in the Netherlands. I spent years on the offensive side of security, hired to break in. Across countless penetration tests and red team engagements, the same pattern showed up: getting in was rarely the hard part. The hard part sat upstream, in the maze of frameworks and compliance an organization had to cross long before anyone touched a single system.
For the better part of a decade, working alongside CISOs and security officers, I watched that maze get worse, not better. NIS2, DORA, ISO 27001, the CRA. More frameworks, more overlap, more evidence to keep current, and almost no tooling that turned any of it into something you operate instead of paperwork you file. The pentest finds the hole. Nobody was helping teams close the gap that let it exist.
That gap is why I built Soveryne. Security you operate, drafted, mapped and evidenced as you work, built by someone who has spent a career finding exactly where things break. And EU-sovereign by architecture, because a compliance program should never be the reason your data ends up under someone else's jurisdiction.
Security that keeps up with machine-speed adversaries.
AI changed both sides. We put it to work for the defender, across the ecosystem: agents that answer from your own controls and frameworks, intelligence that knows what is exploited, and scans that see what an attacker sees.
AI belongs on the defender's side
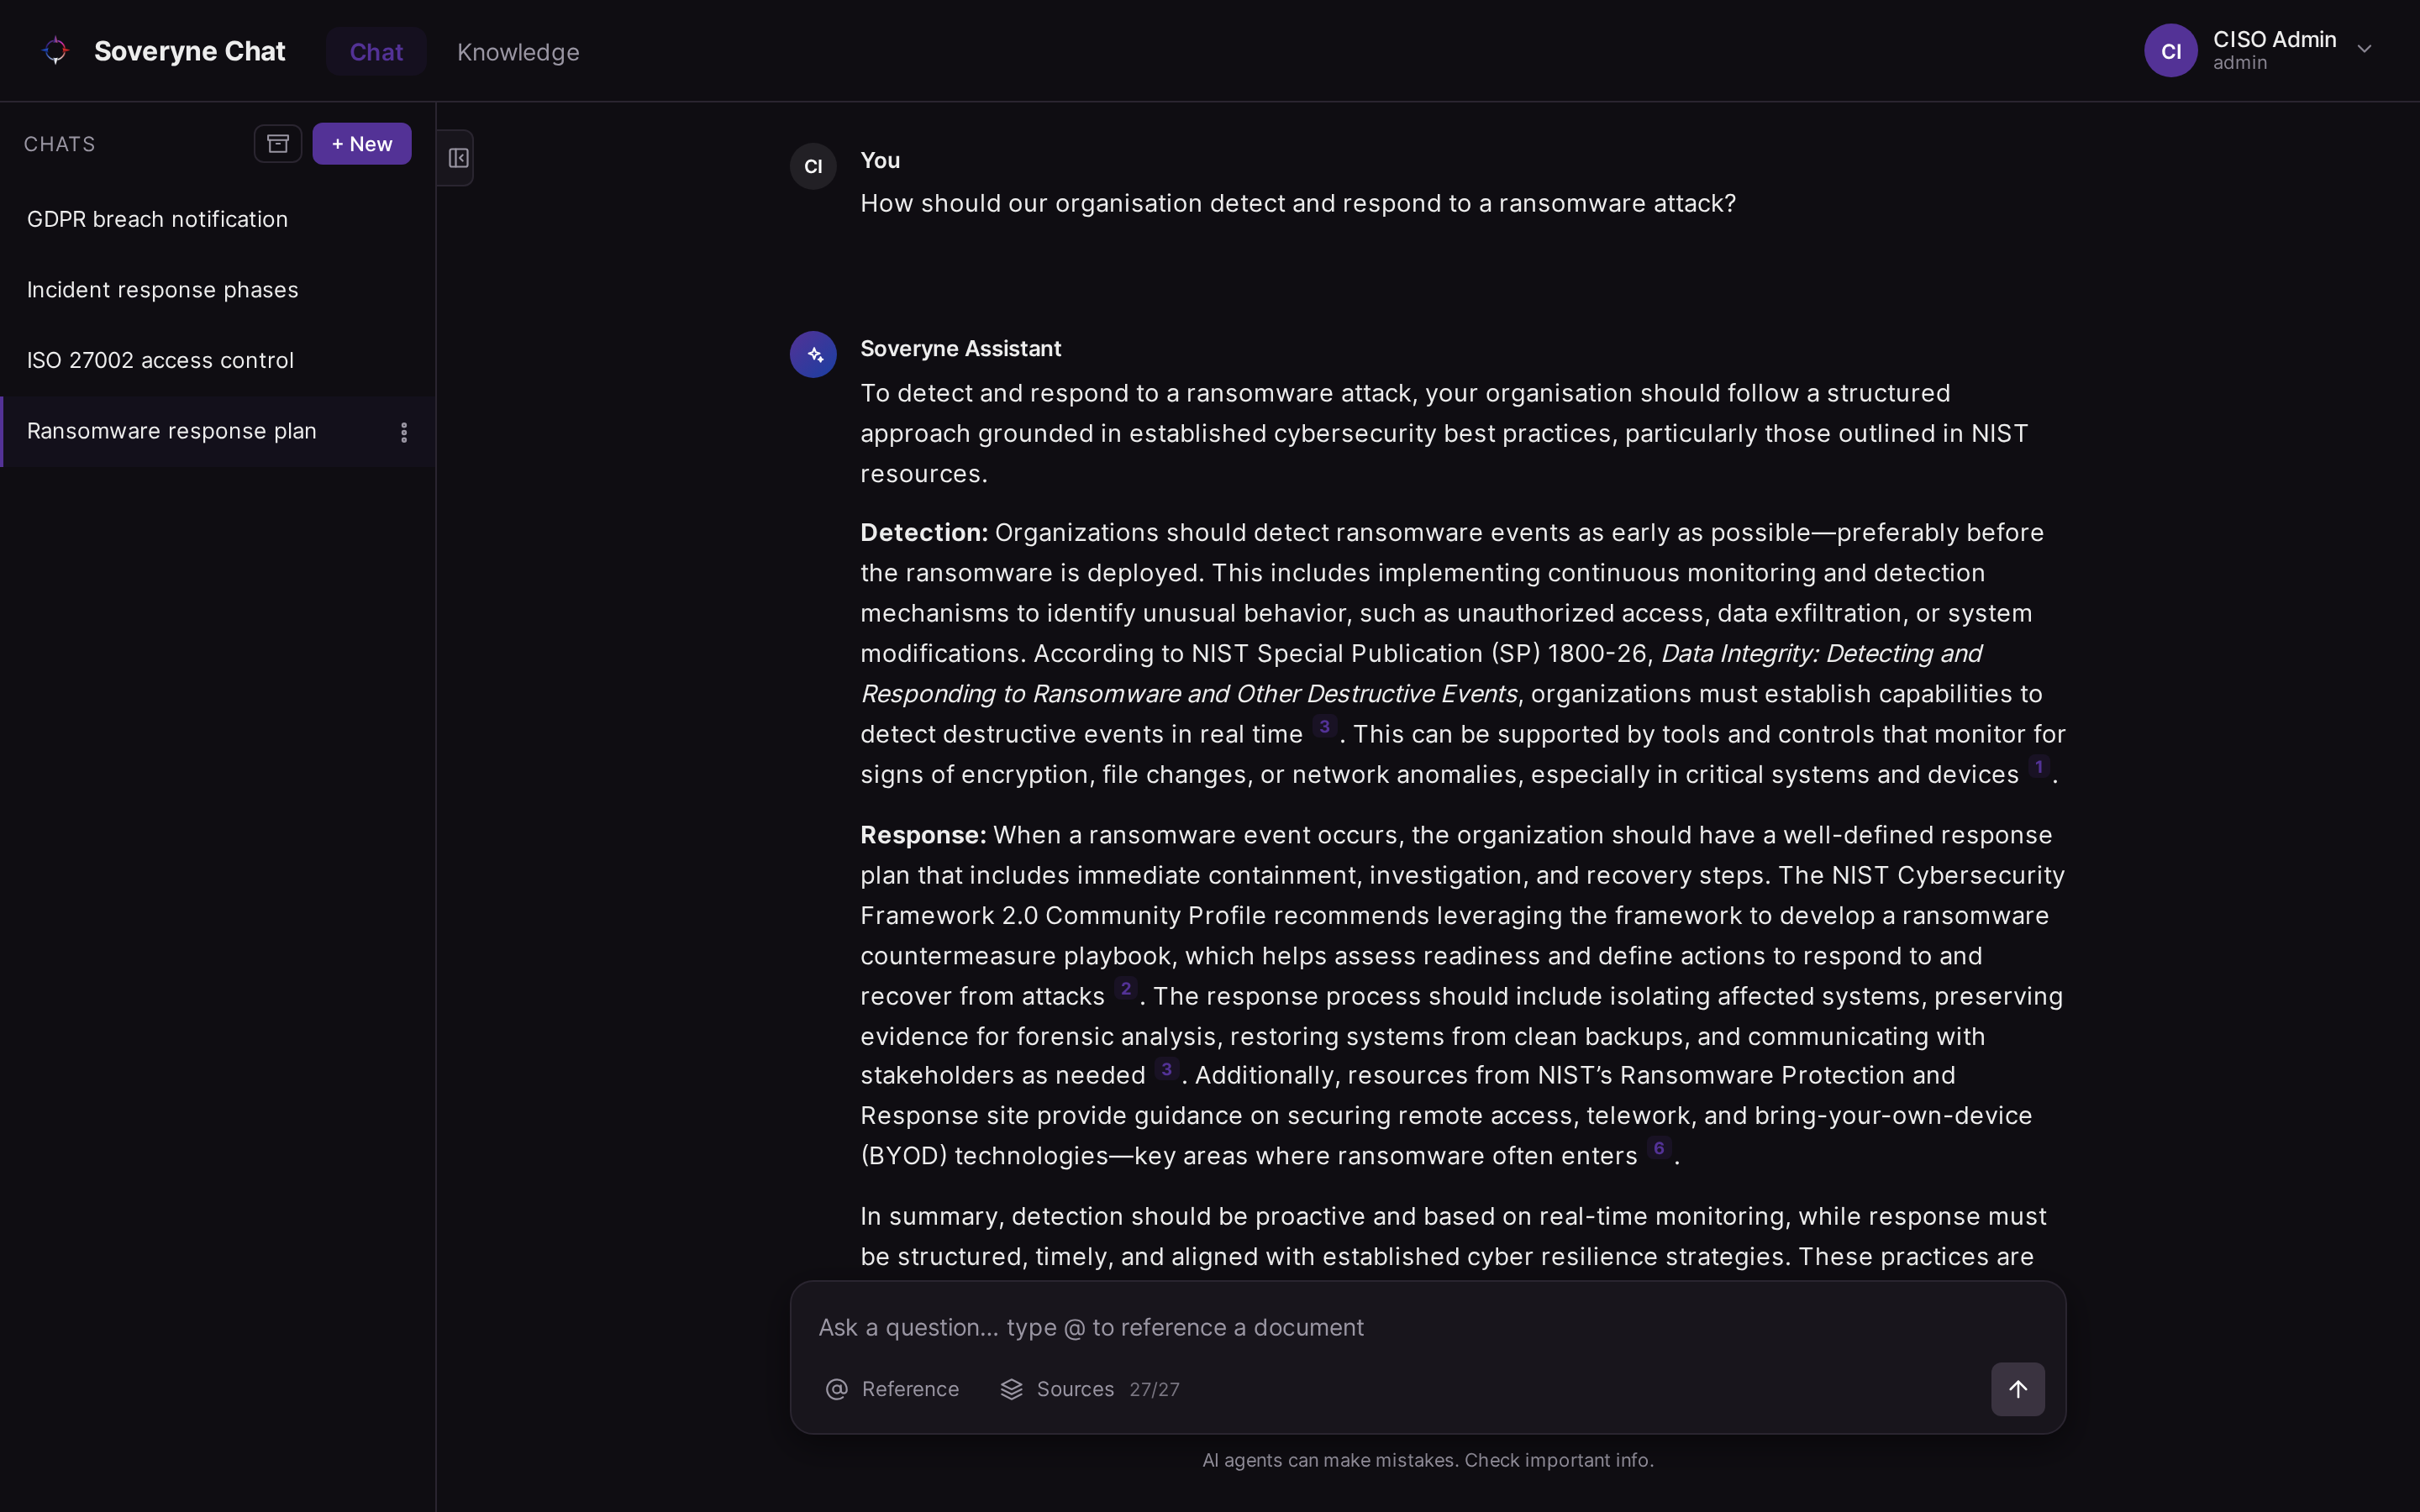
Put your question to the Command agents. They draw on knowledge bases spanning frameworks and laws like ISO 27001, DORA, NIS2 and NIST, and answer in the context of your own controls and assets.
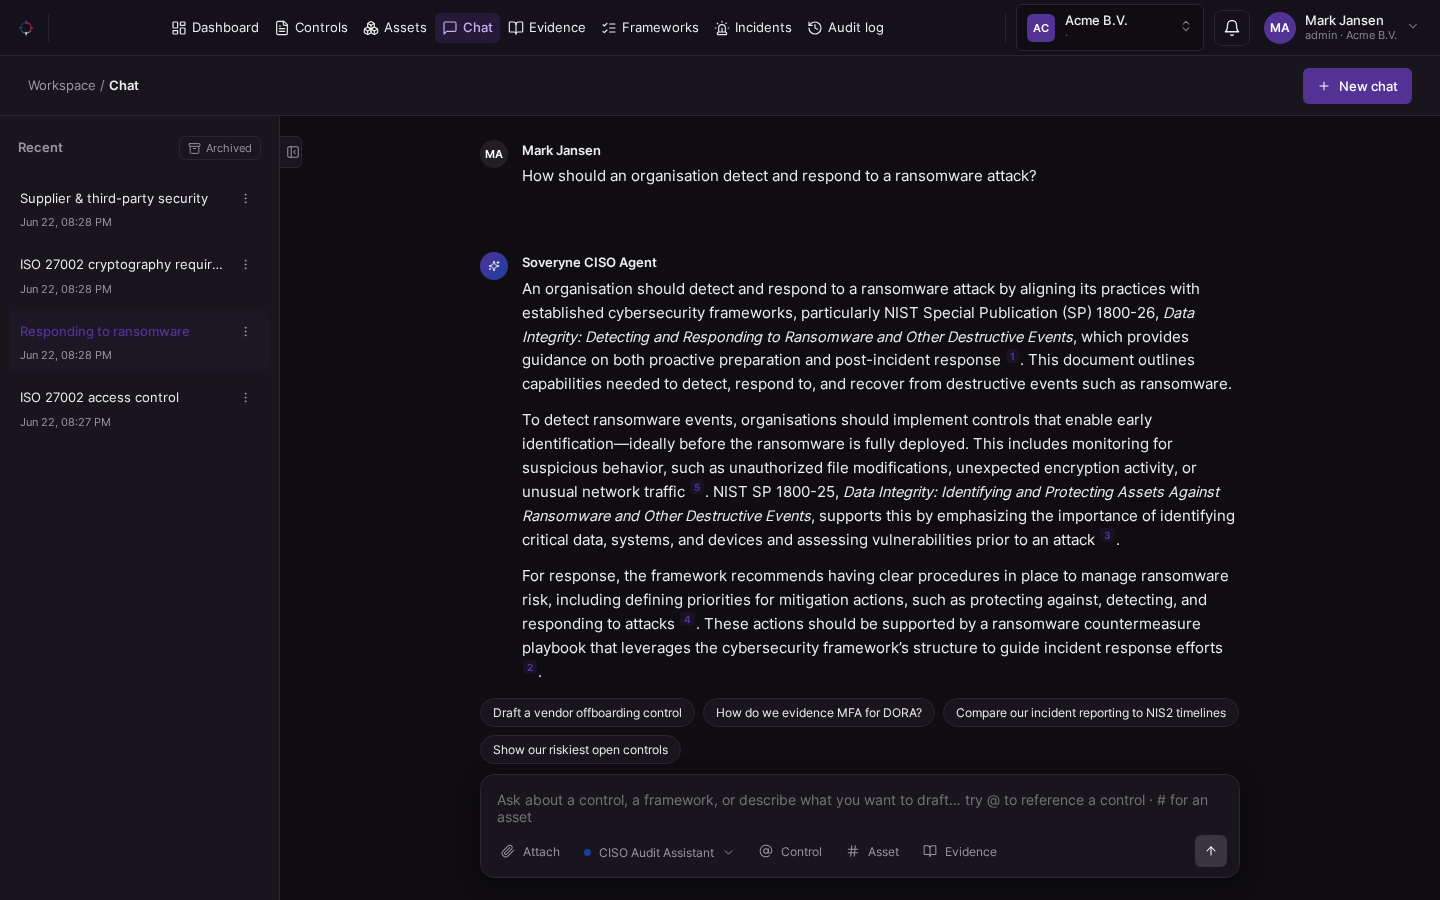
Counsel: answers you can verify
Ask Counsel in plain language and get an answer grounded in your own frameworks and documents, with every claim cited to its source.
Noise is the enemy of response
A curated feed summarized and risk-assessed against your controls and assets, so you act on what matters, not on noise.

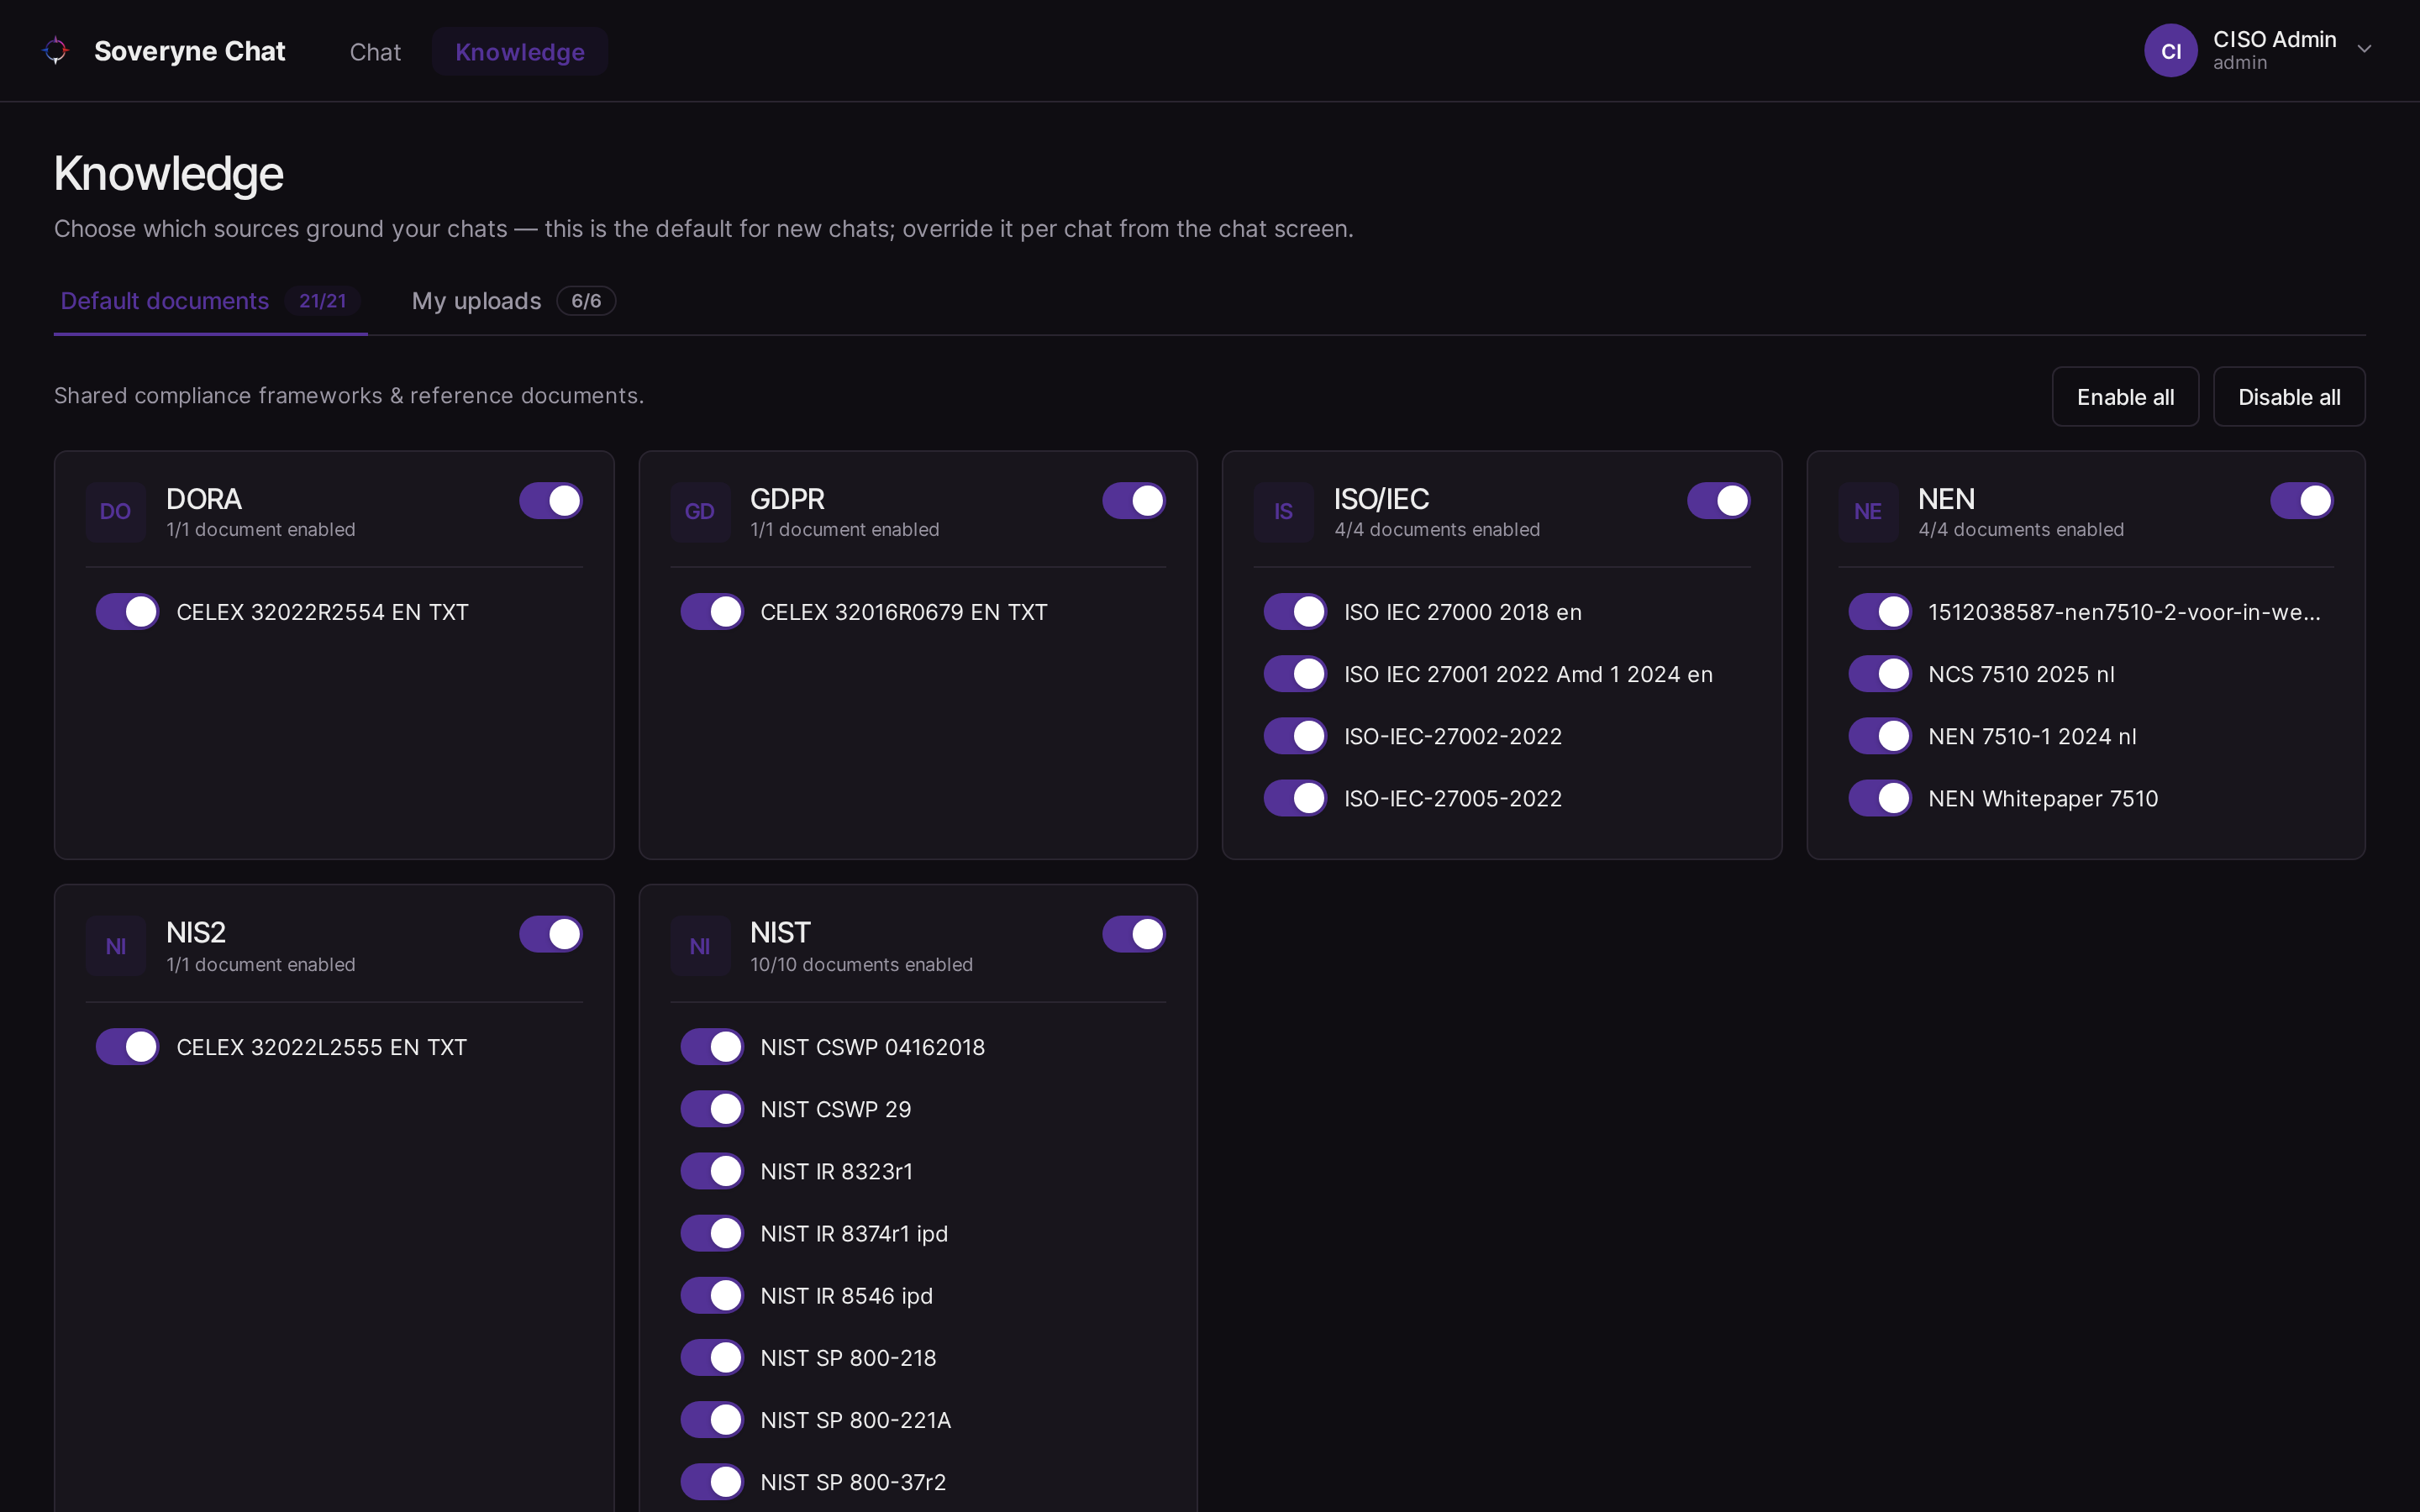
Counsel: a knowledge base that grows
Frameworks and regulations like ISO/IEC, DORA, NIS2, GDPR, CRA, NEN and the Dutch government baseline, ready to answer from today, with more knowledge added over time.
Collaborate, in context
Comment, discuss and review each control right on its page, where the work lives. Every control maps automatically to the assets it protects, the framework controls it satisfies, and its evidence.

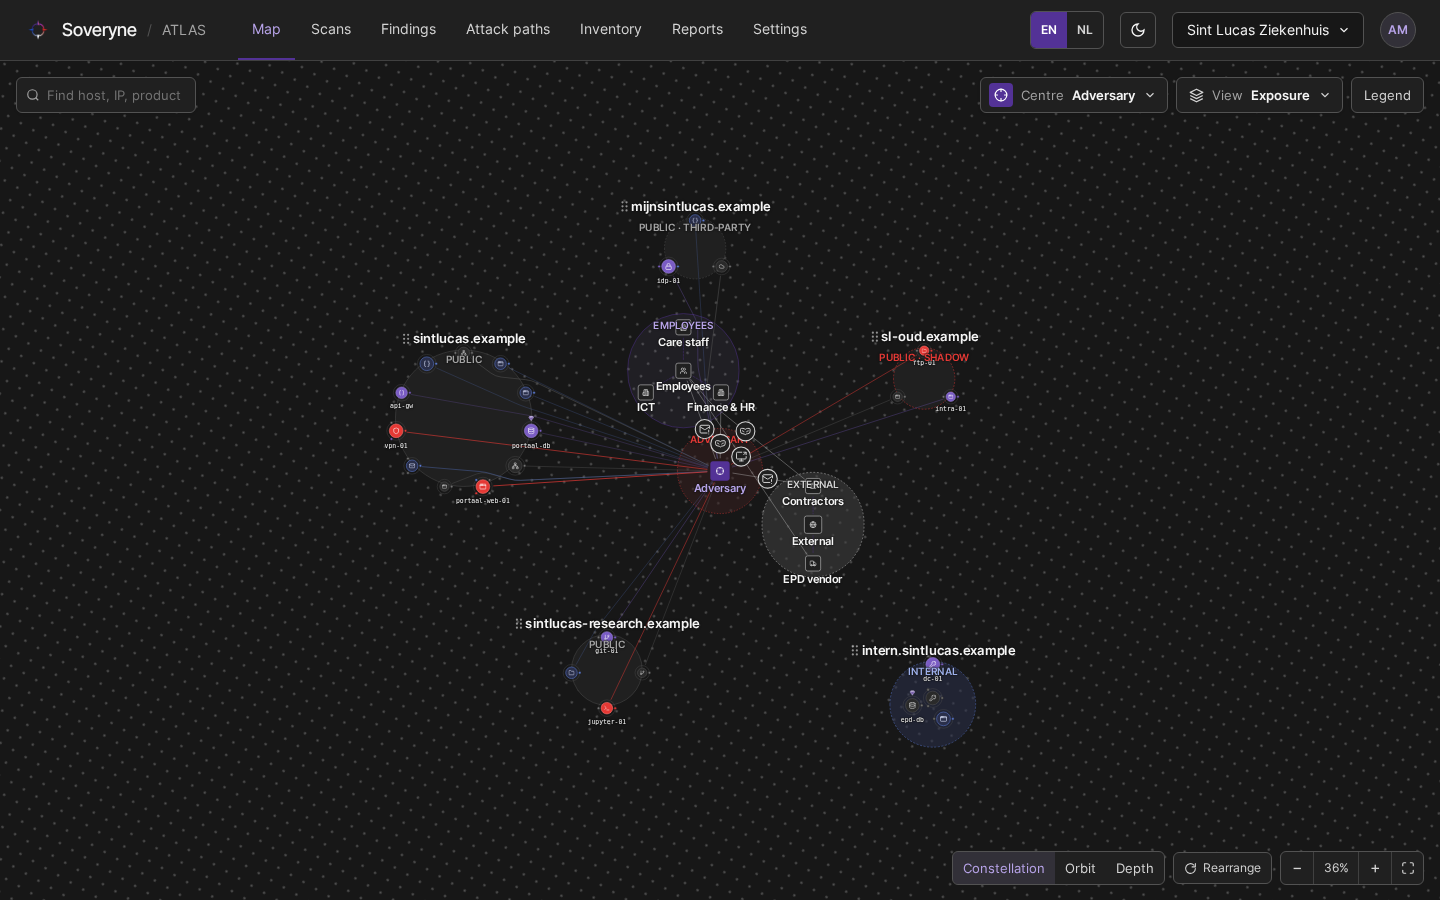
ATLAS: see what an attacker sees
ATLAS maps what you expose to the internet and draws the paths to the systems you cannot lose, annotated with the adversaries SPECTER scores as relevant to you.
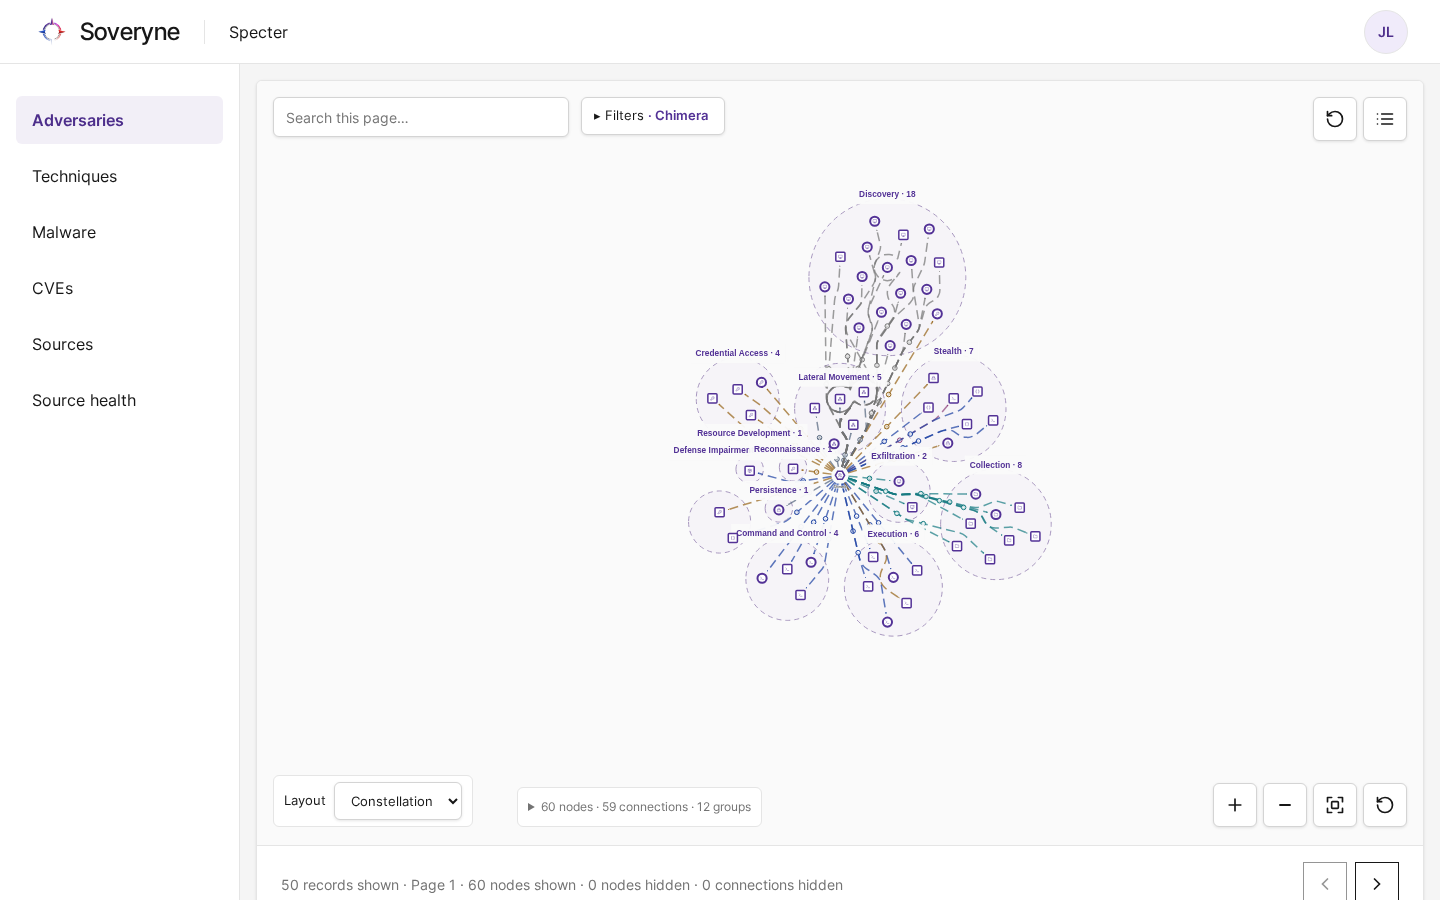
SPECTER: the adversaries that matter
Which vulnerabilities are exploited, and which adversaries would use them against you. SPECTER feeds the same intelligence to ATLAS scans and BAIT exercises.
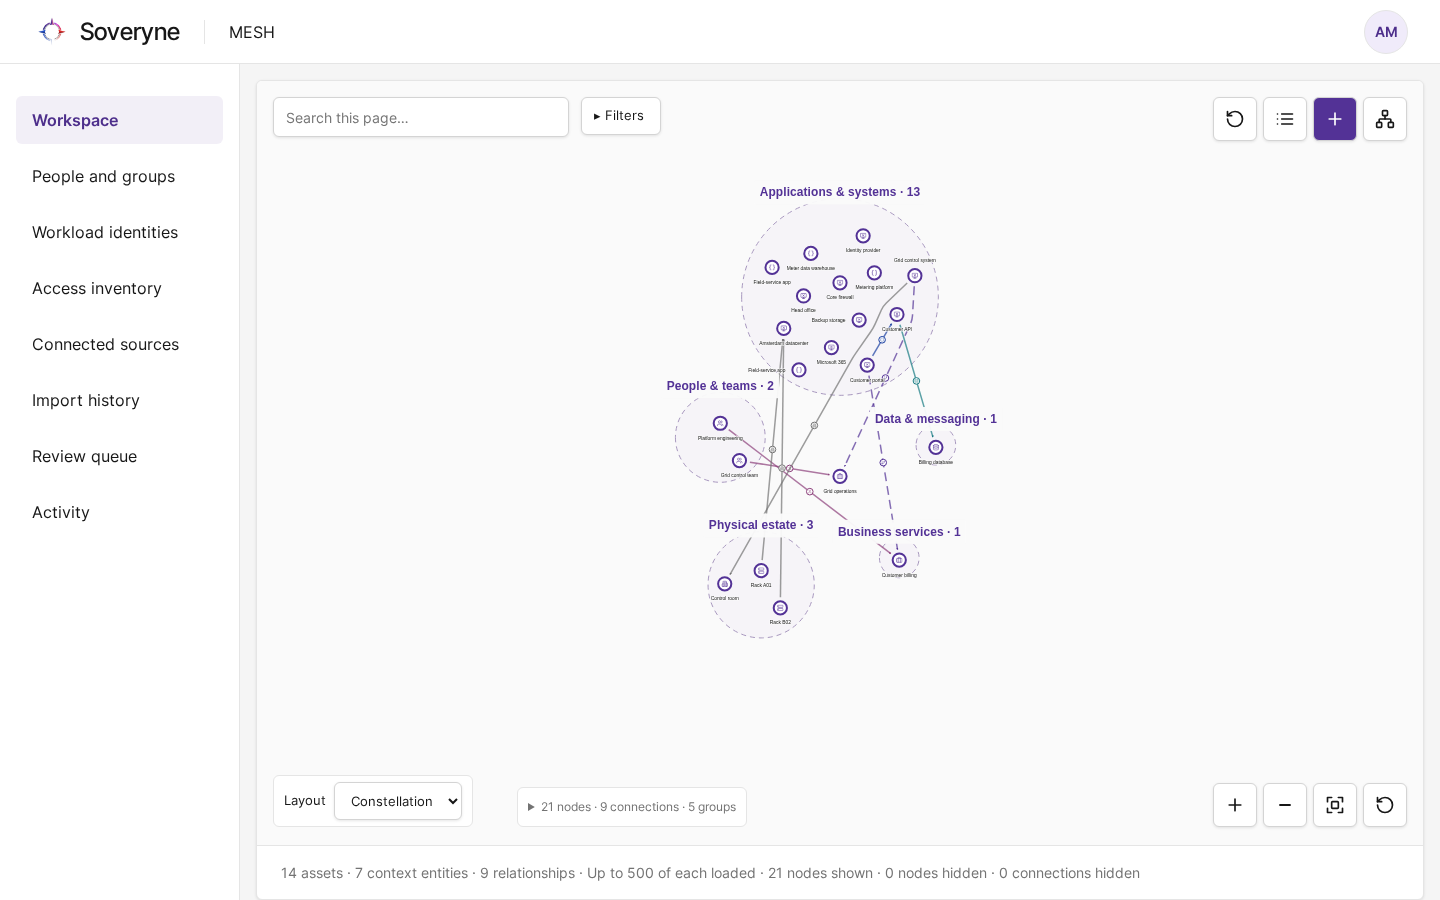
MESH: one register, filled for you
MESH keeps one live inventory of your assets, people and relationships, imported every night from your clouds and CMDB. Command, ATLAS and BAIT all read from the same rows.
BAIT: train against the attacks you face
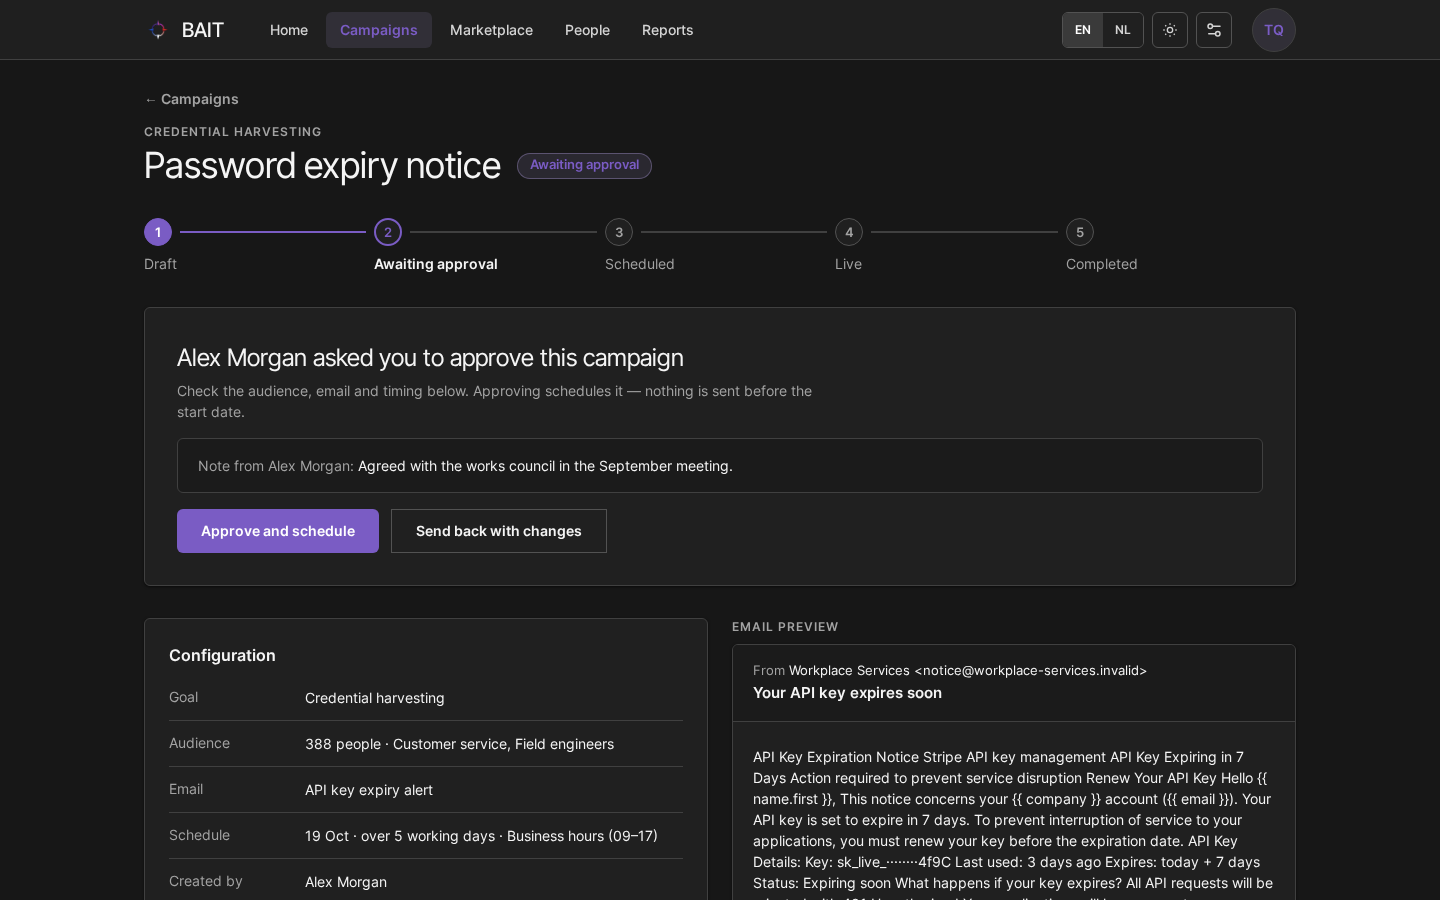
Phishing simulations built on the adversaries SPECTER scores as relevant to you. A second person approves every campaign, and results are reported per group, never per person.
Built in deliberate order, in the open.
One sovereign platform first, then the consoles your teams sign in to and the intelligence they share. All of it is live today. Next is the offense that defense is built on, run autonomously.
- 01 · Live
Platform
The EU-operated platform every product installs into.
- 02 · Live
Consoles
What your teams sign in to.
LiveCommandCISO-as-a-ServiceThe control register, evidence store and policy workshop a CISO runs from.
ExploreLiveCounselGrounded advisory chatAnswers from the actual standards and your own documents, cited.
ExploreLiveATLASAttack surface managementFinds what you expose to the internet, and the paths to what you cannot lose.
ExploreLiveBAITPhishing awareness programmePhishing simulation an auditor and a works council can both sign off.
Explore - 03 · Live
Intelligence
Shared underneath every console.
LiveSPECTERSecurity Profile, Exploit, Campaign & Threat Evidence RepositoryWhich vulnerabilities are exploited, and which adversaries matter to you.
ExploreLiveMESHManaged Entity & System HubOne live asset inventory, filled every night from your CMDB and clouds.
ExploreLiveSAGESecurity Agent Guidance & EmbeddingsTrusted knowledge to start from, extended with your own.
Explore - 0404 · Coming soon
Autonomous offense
Defense by a good offense, at machine speed.
Coming soonZero-day factoryProduces zero-day exploits on demand.
Vulnerability research on demand: exploits for previously unknown flaws in the software you depend on, so you can close what no scanner knows about yet.
Register interestComing soonAutonomous red teamingAutonomous AI that performs red-teaming engagements.
AI agents that plan and run red-team engagements end to end, emulating real adversaries continuously instead of once a year.
Register interest
Continuous validation runs through all of it.
It is core to how we work, not a finish line. Each solution we ship is a step toward the same goal: security that is checked and proven on an ongoing basis, not filed once a year. It is a continuous effort, and every stage moves it forward.
See what Soveryne can run for you.
Get in touch and we will run a free intake, mapping your real posture across the frameworks that apply to you. Not the right fit? We will tell you straight.