
See your perimeter the way an attacker maps it.
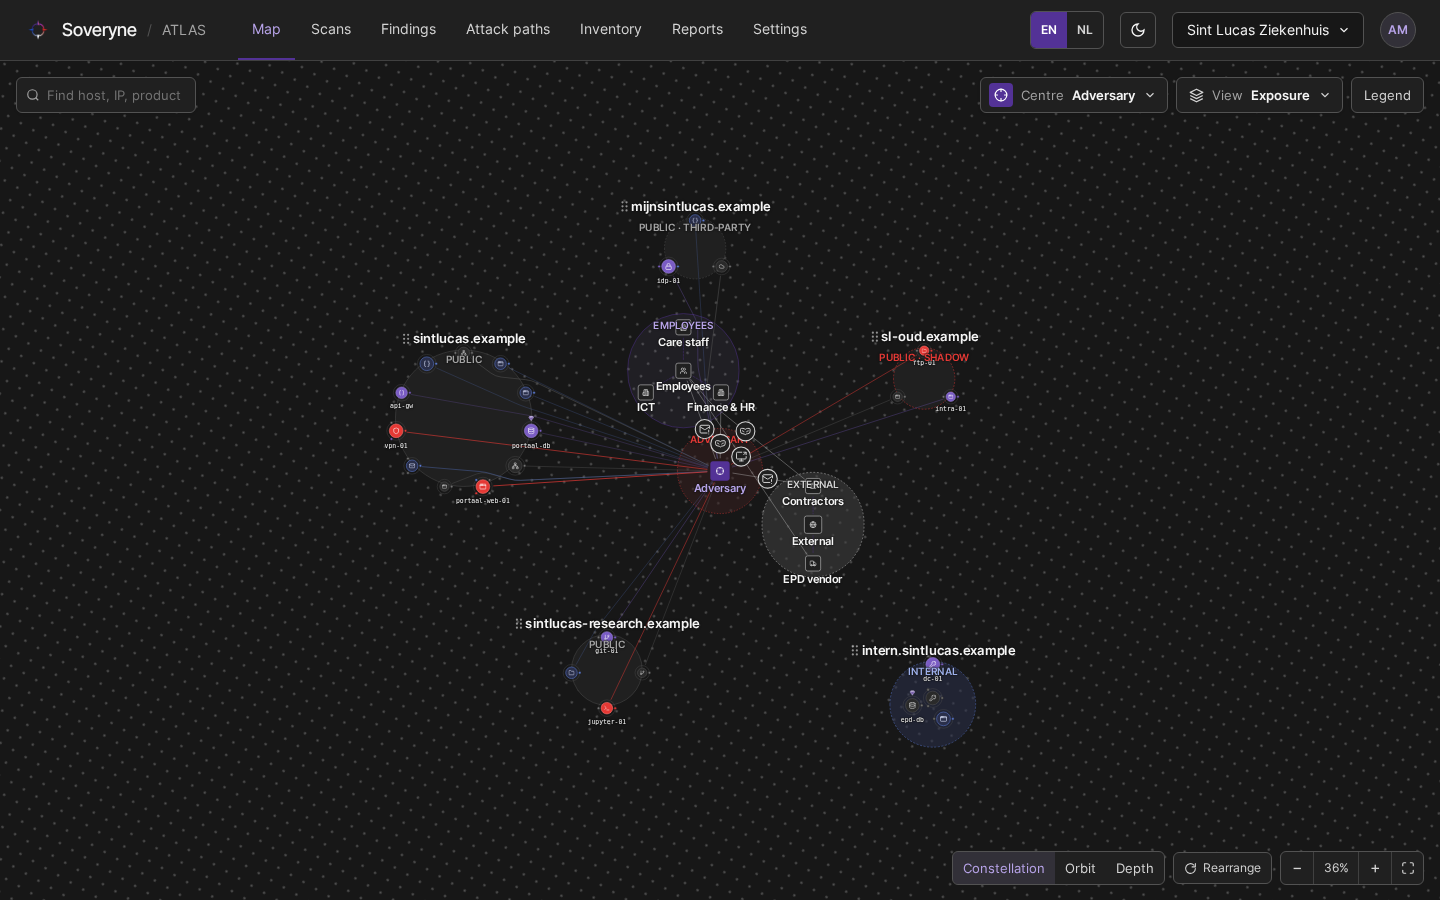
ATLAS finds what an organisation has exposed to the internet, works out which of it is dangerous, and draws the paths to the systems it cannot afford to lose, annotated with the adversaries SPECTER scores as relevant to you. It will not send a packet until a signed mandate and proved domain ownership are both on file.
- Layer
- Consoles
- Pillars
- Technology
- Frameworks
- —
- Pricing
- Quoted with your bundle
ATLAS in the ecosystem.
Finds what you expose to the internet, and the paths to what you cannot lose.
Authorisation is a gate in code
A named signatory, proved domain ownership and a routable address: all three, or the job is refused and the refusal is the audit row.
Passive first, then active
Certificate transparency, DNS and RDAP before anyone signs. Then port and service scanning, fingerprinting and a TLS audit on every TLS service.
Who would use it, and how exploited it is
SPECTER adds CVSS, EPSS and CISA KEV to every observed component. SPECTER ties each asset class to the adversaries and techniques that reach it.
Nothing intrusive by default
Trying a default credential needs a second authorisation: signed, time-boxed and naming its hosts. It is in no built-in profile.
Arrives with MESH, so discovered hosts land on the inventory you already curate. SPECTER powers every scan.
No rate card to decode. Add ATLAS to a bundle and we price it with everything else you choose.
Build a bundle with ATLASHow customers growSee ATLAS on your own environment.
A walkthrough on your systems and your frameworks, with the people who built it.