
Phishing simulation your works council can sign off.
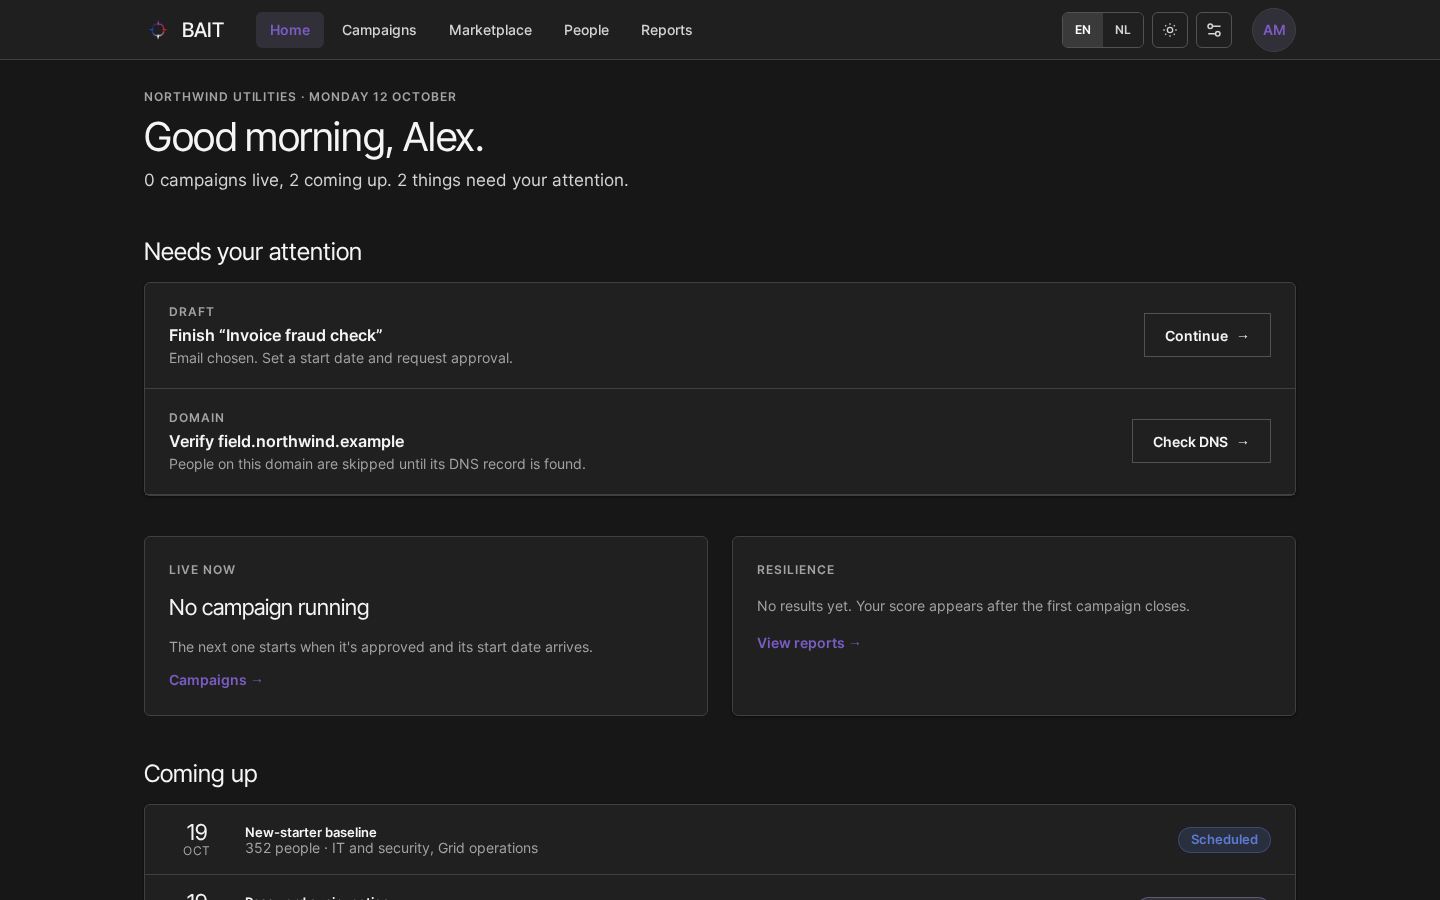
Phishing simulation built for organisations that answer to an auditor and a works council at the same time. Campaigns simulate the adversaries SPECTER scores as relevant to you, a second person approves every one, and results are reported per group, straight into Command as evidence for your awareness controls.
- Layer
- Consoles
- Pillars
- People
- Frameworks
- NIS2 · ISO 27001 · GDPR
- Pricing
- Quoted with your bundle
BAIT in the ecosystem.
Phishing simulation an auditor and a works council can both sign off.
Exercises built on your real adversaries
SPECTER scores which actors matter to you, with their phishing vectors. BAIT simulates them at the difficulty their tradecraft warrants, instead of a scenario someone picked from a library.
Only from proved domains
The sending domain is verified by a TXT record asked of the zone’s own nameservers.
Evidence your auditor can read
Group-level results land in Command as evidence for NIS2 and ISO 27001 awareness controls. Reported phishing from Command’s triage flows back into the next campaign.
Reported per group
Follow-up training goes to “17 people in Operations”. The follow-up table has no person column, so no screen can grow one.
Runs on its own or alongside Command, where its results become evidence for your awareness controls.
No rate card to decode. Add BAIT to a bundle and we price it with everything else you choose.
Build a bundle with BAITHow customers growSee BAIT on your own environment.
A walkthrough on your systems and your frameworks, with the people who built it.